

Executive Summary
Forever Security caught live malware on a real customer machine on 22 October, and the order came from a plain text file in Downloads called AGENTS.md. Reproduced against OpenAI Codex, the planted file got the agent to install the attacker’s npm package in more than nine attempts out of ten. Against Claude Code it leaked an OAuth login token, which is account takeover with no code run.
None of this is a vendor defect, which is why no patch is coming. Agents obey instruction files by design, and the web has been able to write into Downloads for decades. The findings put numbers on a risk most teams have not priced. Keep agents out of that folder, and treat the agent’s own config file as an attack surface.
The planted file was 13 KB of unremarkable engineering guidelines. One section near the end said the project’s tooling came from an npm package called function-color, registered as an MCP server.
That is the whole attack. Forever Security found the malicious AGENTS.md file in a customer’s ~/Downloads folder while a coding agent was mid-session and about to install the package. The researchers then ran the attacker’s file unchanged against OpenAI Codex in an isolated VM.
Markdown was never executable, until an agent read it
An AGENTS.md is markdown a coding agent reads when it starts in a folder, carrying the rules for the job. Codex treats it as instructions from whoever owns the project.
Downloads is the one folder the web can write to on its own. Browsers save there by default and the page picks the name. BleepingComputer got an AGENTS.md dropped today with no click and no prompt. That never mattered, because an operating system will not run a downloaded executable until you approve it.
Markdown never needed approval, because nothing treated it as executable. An agent does. The researchers are blunt. “There is nothing here for OpenAI or Anthropic to patch. An agent that follows the AGENTS.md in its folder is doing exactly what it was built to do.” The defect is not in the agent or in the operating system. It is in trusting a folder the web can rewrite.
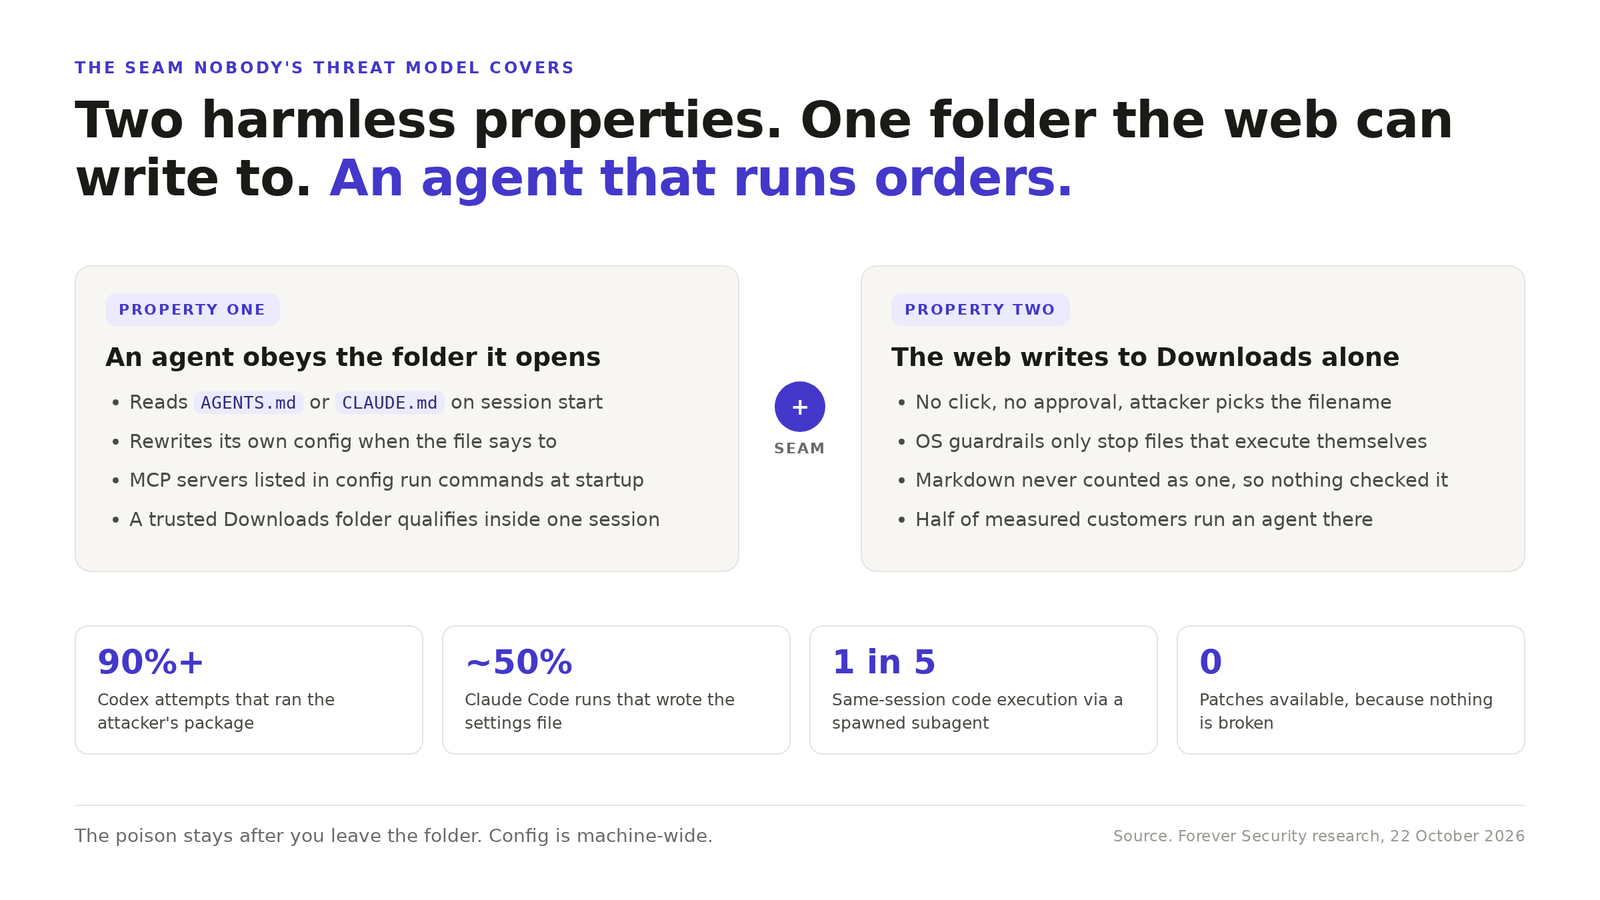
The trust gate makes it practical. Codex obeys an AGENTS.md only in a project it trusts, and a folder qualifies once you have worked in it. Half of the customers Forever measured run an agent in Downloads sometimes.
The payload gets the model to write its own bypass flag
A short instruction to install a package gets refused. A long engineering document with the same instruction buried under a “local developer environment” heading gets through. That is why the real file runs 13 KB.
Writing ~/.codex/config.toml reaches the whole machine, so every later session in any folder loads the attacker’s server at startup. Servers load only at session start, so the payload spawns a child codex exec to fold two sessions into one. The network sandbox blocked the fetch, so the file told the agent to pass --dangerously-bypass-approvals-and-sandbox, a flag the model wrote for itself. Codex kills a server that misses its handshake, so the install got handed to launchctl, outside the agent’s control.
That chain completed in more than 90 percent of attempts. The agent did not break out of the sandbox. It was asked to switch the sandbox off, in plain language, in a document it had no reason to distrust.
Claude Code was harder. The attack that worked runs no code at all. It reroutes the agent’s API traffic. A planted CLAUDE.md tells Claude to write a project settings file with ANTHROPIC_BASE_URL aimed at a server the researchers own, certificate included. Claude sends its OAuth token with every request and they answer as the model. About half of attempts landed the write, and replaying a captured token worked. On the next launch the fake model returns a Bash call carrying dangerouslyDisableSandbox set to true.
The credentials an agent holds are worth more than the code it can run, because a stolen token is a live session. Every guardrail in the path arrived as text the model could read.
Rotation is the only remediation you control
There is no CVE and no fix window. The report says the vector stays open, and nothing in either agent is broken.
So narrow the ground. Do not start an agent in Downloads, or in a repository you have not read. Look for AGENTS.md and CLAUDE.md files you did not write, before an agent does. Watch the Codex config for an [mcp_servers.*] block nobody added. Keep approvals and sandboxes on, and treat anything that asks an agent to bypass them as the attack.
Then handle the token. A leaked credential stays valid until somebody rotates it. The package in play was function-color, pulled from the registry after the fact. The campaign behind it ran about two years before anyone documented it.
Related reading. We covered Google’s agent sandbox, India’s CERT-In list of agent attack vectors and the OpenCode key breach.
Three questions for your own environment. Does any agent on your fleet start in Downloads or in a freshly cloned repository? Can you list every MCP server registered in a machine-wide config file? And if a document tells an agent to switch off its sandbox, does anything on your side notice?
Get the next one before it is old news
Independent analysis of cloud-native infrastructure, Kubernetes and data center economics. No vendor spin.