

Executive Summary
VAST Data announced DataEnclave on 22 September 2026, a confidential AI runtime inside the VAST DataEngine built on NVIDIA Confidential Computing. Models and data are decrypted only inside hardware-isolated enclaves, after cryptographic attestation verifies the environment, the GPU included, and matches it against policy. Data keys stay in the customer’s trust domain, model weights stay in the builder’s, and the infrastructure operator holds neither. The capability is in preview and ships in the first quarter of 2027 through VAST and OEM partners including Cisco and Supermicro.
Attestation is what changes the conversation. Regulated buyers cannot move the data out, and model builders will not put weights on infrastructure they do not control, so the two sides stall each other. Proving the environment before releasing a key is the only shipping architecture that satisfies both at once. What stays open is the trust root behind the attestation and what sealed execution costs in throughput. Both belong in a pilot, not in a datasheet.
The standoff is easy to describe. A bank cannot move customer records to an external AI service. The company that built the model will not hand over weights to run on hardware it does not control. The tie breaks with confidential computing, which removes the operator from the trust boundary using hardware instead of a contract clause. VAST Data put that runtime inside its own data platform, and named the partners it needs to make it real.
Attestation turns a promise into a check
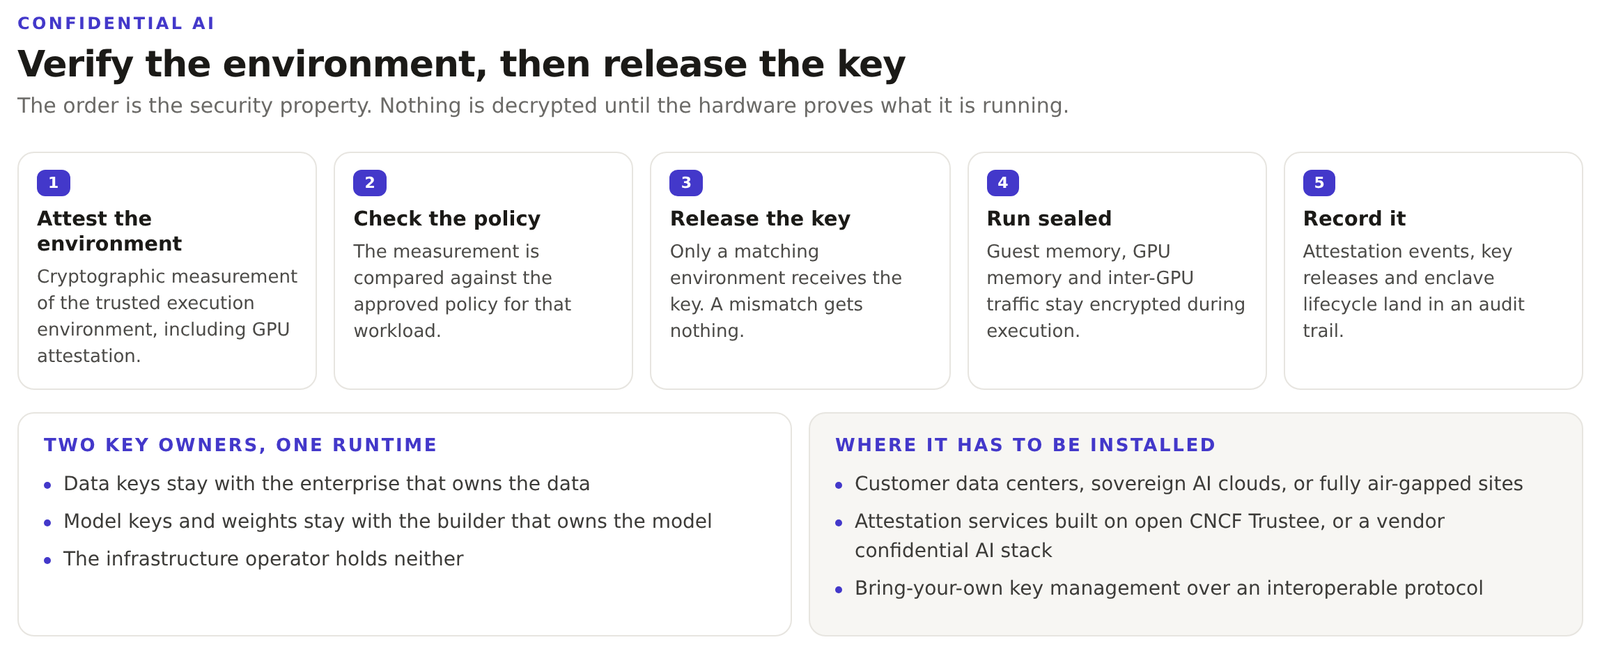
Conventional encryption protects data at rest and in transit, and stops there. Confidential computing extends encryption to the moment of execution. DataEnclave uses NVIDIA Confidential Computing to create a secure container runtime inside the VAST DataEngine. Guest memory, GPU memory, and the links between GPUs stay encrypted while a model runs, and the workload is isolated from infrastructure operators, administrators, and other tenants sharing the same hardware.
The order of operations is the security property. The runtime verifies the trusted execution environment before it releases anything, and a measurement that does not match the approved policy gets no key. Attestation events, key releases, and enclave lifecycle actions are written to an audit trail in the VAST data warehouse, so a reviewer can see which workload ran under which policy without seeing the data or the weights.
Two key owners is the part procurement will care about
Most confidential designs protect one side. This one separates two. Jeff Denworth, co-founder at VAST Data, put the commercial case plainly, saying that model weights are fast becoming the most valuable intellectual property in the world. He is arguing from the builder’s side, and the architecture follows his logic. Enterprise data keys stay under customer control, model keys and weights stay inside the builder’s trust domain, and key management is bring-your-own over an interoperable protocol. Neither side has to trust the other’s operations, which is what makes a shared environment acceptable to both.
The deployment options follow from that. DataEnclave runs in customer data centers, in sovereign AI clouds, and in fully air-gapped sites, with attestation services built on the open CNCF Trustee stack or through a partner confidential AI offering such as Fortanix. NVIDIA’s confidential computing is in its third generation across Hopper, Blackwell, and Rubin platforms, so the hardware floor is real. A fleet that predates those parts is looking at a refresh, not a software upgrade.
Ask what the enclave costs before you believe the demo
Three things belong in a pilot. The first is the trust root. Attestation is only as good as the thing that signs the measurement and the process that decides what counts as an approved policy, and that is an operational problem more than a cryptographic one. The second is throughput. Confidential virtual machines and encrypted interconnects are not free, and the only number worth having is the one your own workload produces. The third is metadata. The audit trail records which workloads ran and under what policy, which is exactly what a regulator asks for and also a new dataset to govern.
Preview status is the practical constraint. DataEnclave ships in the first quarter of 2027 through VAST and OEM partners, with Cisco and Supermicro named at launch. Model makers including Cohere, CrowdStrike, Deepgram, and TwelveLabs are building against it now. That gives a regulated buyer a runway to design the pilot, and a reason to ask their own storage and GPU vendors what the equivalent answer is.
Three questions for the next briefing on this. Which parts of the stack does the attestation actually cover today? Who controls the policy that decides when a key is released? And what does sealed execution cost per inference hour once the enclave overhead lands in the bill?
Related reading. Workload sovereignty is the question procurement cannot answer sets out what a buyer can actually test. The argument that storage is the gap in every infrastructure newsroom explains why the data layer keeps deciding AI outcomes.
Get the next one before it is old news
Independent analysis of cloud-native infrastructure, Kubernetes and data center economics. No vendor spin.
[…] Read the full analysis, The Only Way to Prove You Cannot See the Data Is to Attest the Hardware. […]