

Executive Summary
September 2026 is a change in the shape of Windows maintenance, not one bad month. Microsoft has now shipped more than 2,700 fixes this year, roughly double its full year record from 2020, on a monthly trend line that ran 161, 220, 663, 457 and then 974. Volume at this scale breaks the assumption that a patch cycle can be triaged by hand inside a single maintenance window.
The consequential detail is coupling. The release interfered with Hyper-V host folder sharing inside Linux guests, which means a Windows update reached past the host into guest behaviour. For teams running Hyper-V beside containers, or weighing it as a VMware alternative, the blast radius of a routine update has become a platform question. Triage by exposure and reachability, stage the rollout in rings, and hold a rollback plan.
Microsoft shipped its largest patch batch on record this month. Then it had to send a second update to repair the first one.
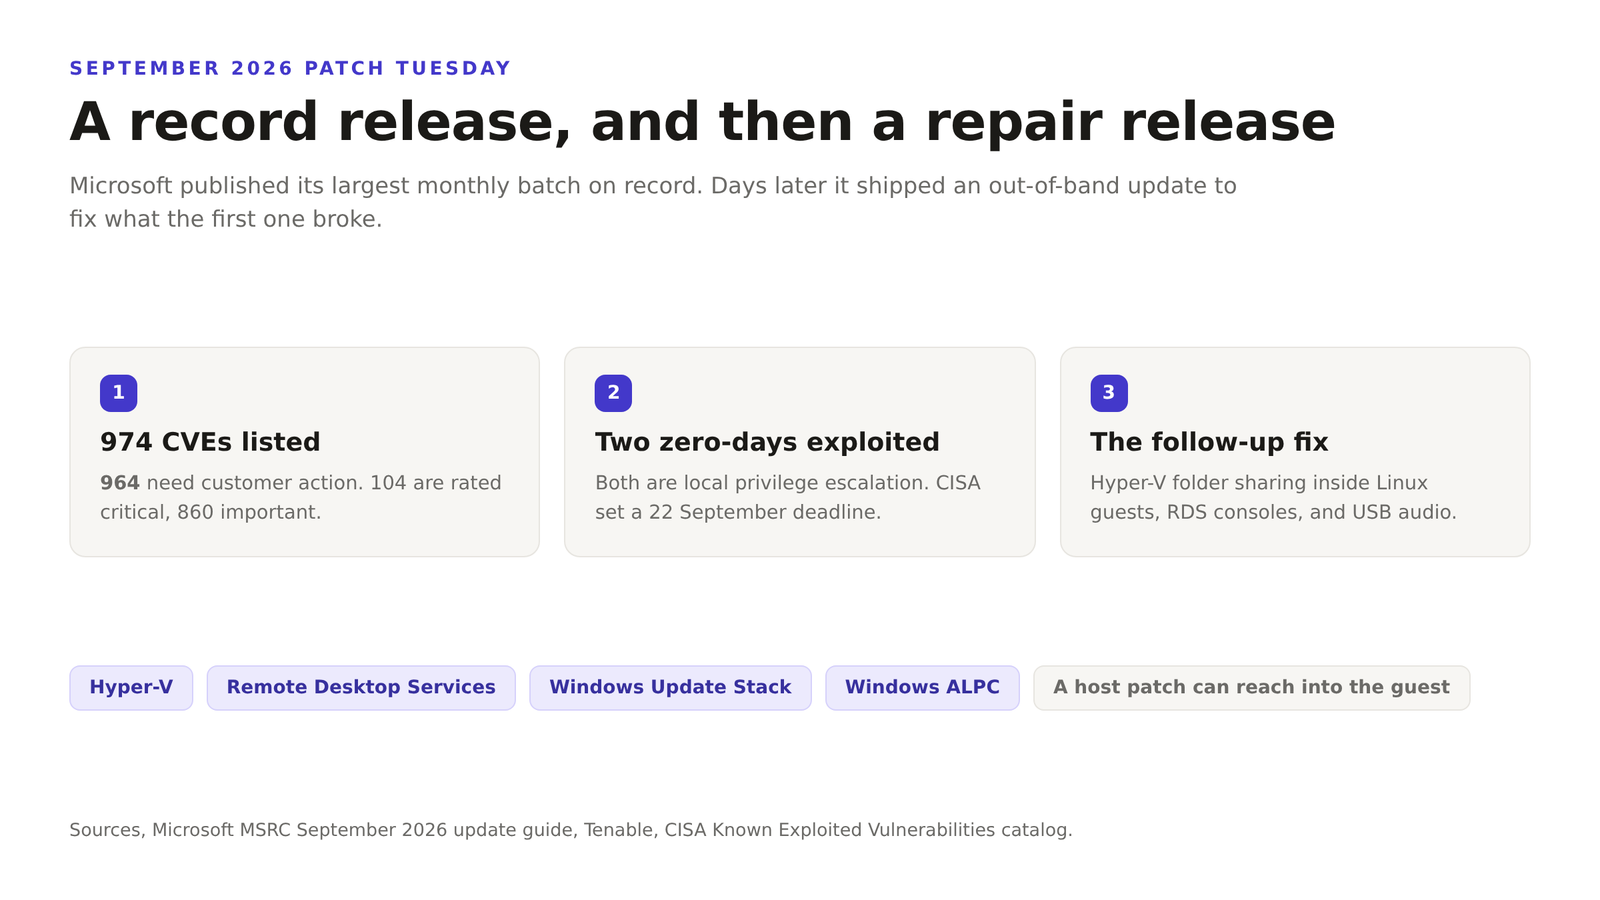
The September 2026 Patch Tuesday release listed 974 CVEs in its September security release, the largest monthly batch Microsoft has ever published. Ten of those are cloud-side fixes Microsoft applies itself, which leaves 964 that customers actually have to patch. It also confirmed that two flaws were already exploited in the wild. Days later, an out-of-band update fixed Remote Desktop Services, Hyper-V host folder sharing, and USB audio that the main release had broken.
The volume is the story
More than 100 of the fixes carry a critical rating. Two matter most. CVE-2026-85880 is a heap overflow in Windows ALPC that lets a local attacker climb to SYSTEM. CVE-2026-81963 is a link resolution flaw in the Windows Update stack. Both were exploited before a patch existed, and CISA added both to its Known Exploited Vulnerabilities catalog with a 22 September deadline for federal agencies.
The count itself has become a problem. Security researchers point to a jump in discovery, much of it powered by automation, and to a patch load that no operations team can triage by hand inside one maintenance window. Nearly 90 percent of this month’s flaws fall into three buckets, privilege escalation, remote code execution, and information disclosure.
The scale is not an outlier any more. Microsoft has already shipped more than 2,700 fixes this year, roughly double its previous annual record from 2020. Automation on the defender side is finding more, and automation on the attacker side shortens the gap between a patch landing and a working exploit. Volume is the new normal, and it changes how a team should staff a patch cycle.
The patch reached into the hypervisor
The follow-up update is the part virtualization teams should notice. Microsoft said the original release interfered with Hyper-V host folder sharing inside Linux virtual machines, and with multichannel USB audio. It also left some Remote Desktop Services consoles unresponsive.
That is a small, specific failure with a large lesson. A host level patch can break guest behaviour, and the blast radius grows with the size of the release. Teams running Hyper-V next to containers, or weighing it as a VMware alternative, have to test at the host layer and not only inside the guest.
There is a version of this that matters beyond Windows. Hyper-V is one of the platforms IT leaders weigh when they leave VMware, and it is also the substrate under Windows Server clusters and Azure Stack HCI. A patch that disturbs host level sharing hits all of it. Teams that treat the hypervisor as a stable layer beneath the noise should update that assumption.
The two exploited zero-days deserve their own note. Both are privilege escalation flaws, which means the attacker still needs a foothold first. That lowers the urgency inside a locked down environment and raises it for anything shared or multi-tenant. Prioritize by exposure, not by the headline count.
How to run a month like this
Patching everything on day one is now a risk of its own. The teams handling this well prioritize by risk, stage the rollout in rings, and keep a rollback plan ready before the last tier moves. The CISA catalog gives you the short list that cannot wait. Everything else can earn its place in a ring.
Inventory helps too. If you cannot answer which hosts still expose the old Remote Desktop role, or which clusters share host folders with Linux guests, you cannot scope the blast radius of a bad update. The month something breaks is the wrong month to build that list.
Microsoft also pushed servicing stack updates rated critical for Windows Server 2012, Windows Server 2012 R2, and Windows Server 2016, plus Windows 10 version 1607. Those older platforms are the ones organizations keep running while they plan a migration, and a critical servicing stack update is not optional on a box already past mainstream support.
The broader signal is that patch volume and infrastructure coupling are both climbing. When a monthly Windows update can disturb a hypervisor, the maintenance window stops being a formality. It becomes a change to the platform your workloads sit on.
Related reading. Our coverage of the vCenter flaw CISA tied to ransomware gangs and the licensing squeeze pushing teams off VMware Cloud Foundation.
Get the next one before it is old news
Independent analysis of cloud-native infrastructure, Kubernetes and data centre economics. No vendor spin.
[…] covered the record release and the repair that followed in full. The lesson travels further than Hyper-V. If a monthly update can disturb a hypervisor, the […]
[…] reading. We covered the client-side half of this month in Microsoft’s record Patch Tuesday, and the kernel bugs that landed the same week in four Linux root flaws at […]