

Executive Summary
A stolen application secret, not a stolen password, opened 162 Microsoft 365 tenants between 13 and 17 October. ConnectWise Cloud Backup is a legitimate product, consented inside customer tenants so it can read mail, files and Teams chats. An attacker used its client secret to authenticate as the application itself. No user signed in, so multi-factor authentication and user-facing conditional access had nothing to challenge. Huntress confirmed 162 compromised tenants by the evening of 16 October. Todyl tied the sign-ins to one hosting address and to a script walking tenants in sorted order.
The count is not the finding. The finding is that the standard response misses the target. Revoking user sessions leaves application access intact. Disabling the app stops new tokens, yet tokens already issued stay valid for up to 90 minutes, and nothing planted elsewhere is removed. In one tenant a second ConnectWise app granted itself Global Administrator, then added client secrets to two other applications, one of them a security vendor’s own tool. Treat the disabling step as the start of incident response, not the end of it.
The backup product did its job honestly for years. Customers granted it tenant-wide permission because a backup tool needs it. Read every mailbox, every OneDrive and SharePoint site, every Teams chat. It needed write access too, since restore is the point. That is a lot of reach for one application.
On 13 October the same hosting address opened with a password spray against four law firm tenants. Nothing landed. On the morning of 15 October, early in the ConnectWise Cloud Backup breach, it stopped attacking people and started using the app instead.
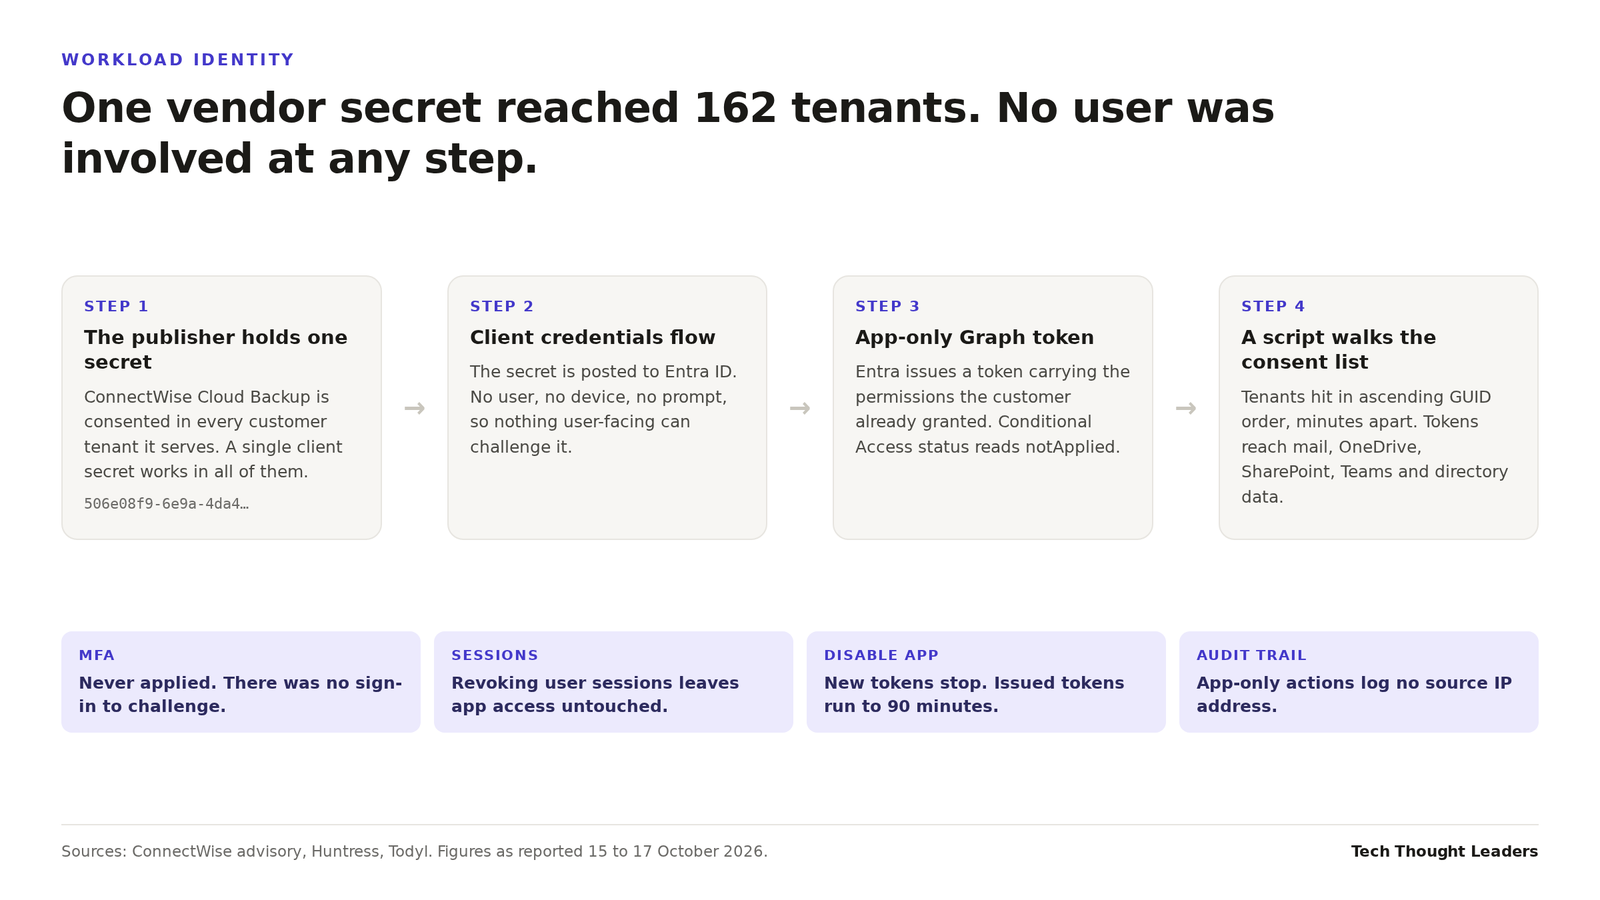
The OAuth client credentials flow is the part worth understanding. The publisher holds a secret in its own tenant, posts that secret to Microsoft Entra ID, and gets back an access token for the customer tenant. No user, no device, no prompt. Entra recorded the sign-ins with conditional access marked notApplied, since there was no user policy to apply to a machine talking to a machine. The token arrived carrying every permission the customer had already approved.
One secret was the entire attack surface
Huntress tracked the sweep at seconds apart per tenant, in sorted order, which is what a script working through a list looks like. Todyl saw tenants hit one to six minutes apart in ascending order, with a 43 minute gap mid-run. Both point the same way. Somebody held a list of consenting tenants and walked it, and Todyl’s read is that every tenant with the app enabled should be assumed compromised.
That is the structural trouble with workload identity. A user credential is useful in one place. An application credential is useful everywhere the application is installed. One secret, 162 tenants, no per-tenant work required.
Every control operators reached for missed the target
The instinct after a breach like this is to force password resets and revoke sessions. Neither touches the path. Session revocation ends refresh tokens tied to users, and the attacker never had one.
Disabling the app is better and still incomplete. It stops new token issuance in that tenant. Tokens already handed out keep working until they expire, which Todyl puts at up to 90 minutes. Disabling also changes nothing about credentials the attacker added to other applications while the door was open.
Huntress found that second phase in a customer tenant. At 03:44 UTC the Cloud Management app for Teams added itself to the Global Administrator role. It then ran a Python script that added client secrets, set to expire in 2028, to an MSP management application and to Huntress’s own tool. Six of nine changes went through. The one that failed was a certificate Microsoft rejected on a thumbprint mismatch. The successful ones sit in that tenant until somebody removes them, a textbook case of the persistence technique MITRE files under additional cloud credentials.
Audit application credentials before mailbox activity
The visibility problem is worse than the access problem. Microsoft’s audit log records app-only actions without a source IP. Directory reads through Graph leave no record at all. Todyl’s own conclusion is that the absence of confirmed exfiltration is partly a logging limit rather than a clean result. Where backup service and attacker share one application identity, logs cannot separate them.
What actually moves the needle is small and dull. Search Entra for the application IDs, review every application for credentials added since 13 October, and get written confirmation that the publisher rotated its secret. Microsoft’s documentation on application objects and service principals is the place to start if anyone on your team needs the difference between the app and the local identity spelled out.
Then ask the question the event raises. How many third-party applications in your tenant hold tenant-wide read and write on mail, and who reviews their credentials on a schedule? Most teams can answer the first half.
Related reading. We covered the governance side of the same problem when ServiceNow argued every AI agent should carry a signed passport, and India’s CERT-In put a secrets audit at the center of its guidance on AI agent attack vectors. Both rest on the same assumption this breach broke.
Sources. ConnectWise advisory, Huntress and Todyl.
Get the next one before it is old news
Independent analysis of cloud-native infrastructure, Kubernetes and data center economics. No vendor spin.
[…] Read the full analysis. […]