

Executive Summary
Five Container Runtime Interface vulnerabilities were patched in containerd on June 18, and three were rated critical. The worst lets anyone who can create a pod import a crafted checkpoint, force containerd to pull a malicious image, and tag it locally. Another pod on that node then runs the poisoned image under its own identity. AWS Security Bulletin 2026-046 lists the affected versions, and containerd underpins Amazon EKS, Amazon ECS, AWS Fargate, Bottlerocket and Amazon Linux.
A second wave landed in September. CVE-2026-53495 is a goroutine leak in CRI ExecSync that a long-lived background process behind an exec probe turns into node-level memory exhaustion. Fixed builds are 1.7.35, 2.0.12, 2.2.8 and 2.3.5. Managed fleets patch themselves, though many still need node recycling. Self-managed clusters wait on you. The pattern across both waves is unglamorous. Isolation is a stack of assumptions, and the runtime keeps trusting metadata it should not.
Kubernetes gets the credit for isolation. The runtime does the work. Each containerd CRI vulnerability in this story sits in that gap.
None of the June advisories needed a kernel exploit. That is what makes them worth reading.
The dangerous bugs were about metadata, not escapes
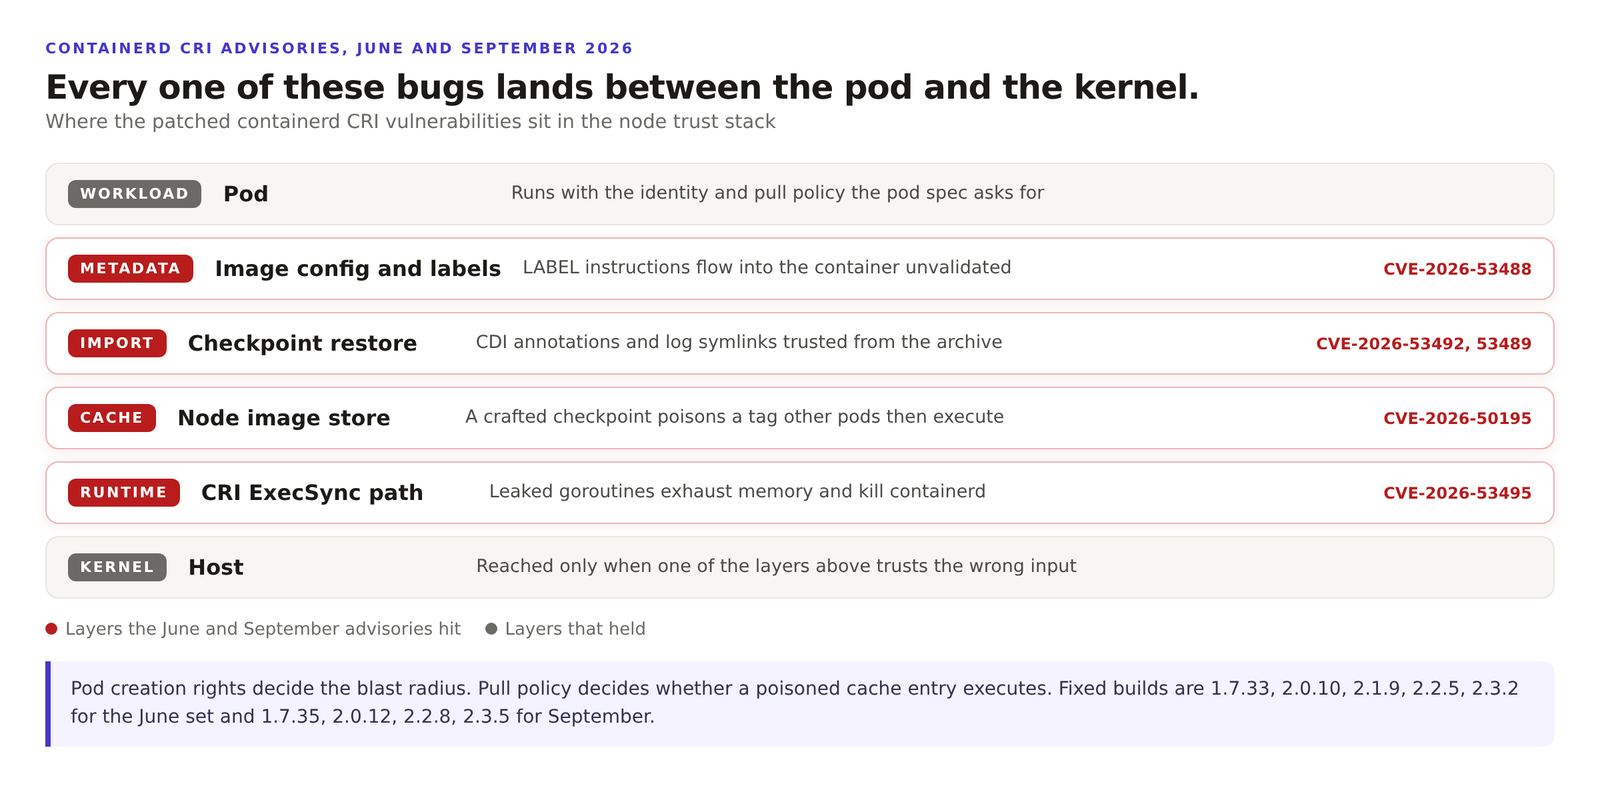
CVE-2026-53488 propagates label instructions from an image config into a container without validation, which can end in command execution on the host through plugins that consume container labels. CVE-2026-53492 trusts Container Device Interface annotations buried inside a checkpoint archive, which allows device or host mount injection where CDI is enabled. CVE-2026-53489 restores container logs through an unvalidated symlink, so kubectl logs can read files it should not reach.
The image cache bug is the one to sit with. CVE-2026-50195 exploits CRI checkpoint import. An attacker with permission to create pods imports a crafted checkpoint, containerd pulls an image it should not and writes it under an arbitrary local tag, and the node’s cache is now poisoned. Any pod on that node using IfNotPresent or Never as its pull policy later runs the attacker’s image while believing it has the legitimate one.
That turns a routine permission into a write primitive against shared node state. Pod creation is common. It is handed to CI jobs, service accounts, and platform tenants. The blast radius is not one workload. It is every workload that lands on that node afterwards.
CVE-2026-47262 rounds out the set. A crafted image exhausts memory until the containerd process is killed, which takes the runtime API down with it and disrupts anything that talks to it. The fixed builds are 1.7.33, 2.0.10, 2.1.9, 2.2.5 and 2.3.2 depending on the release line. The Kubernetes CVE feed is the list worth watching weekly.
Patch the runtime, then ask who can create pods
The September bug is narrower and still nasty. CVE-2026-53495 leaks goroutines in the CRI ExecSync path when exec probes or lifecycle hooks spawn background child processes that outlive the probe. Repeat that often enough and containerd runs out of memory and gets killed. Tencent’s Xuanwu Lab reported it. Fixes shipped in 2.3.5, 2.2.8, 2.0.12 and 1.7.35, and the workaround is to keep probes from launching long-lived children.
Version checks matter more than they look. The runAsNonRoot evasion disclosed in May, CVE-2026-46680, was fixed in 1.7.32, 2.0.9, 2.2.4 and 2.3.1, with no patch for the 2.1 line because it had reached end of life. A cluster pinned to an unmaintained branch will not receive these advisories through an upgrade, no matter how good its scanner is.
Managed Kubernetes hides this work and defers part of it. AWS said it deployed patched runtimes across affected managed fleets and that self-managed users on EC2 or on premises must upgrade themselves. Node recycling is the step people skip. A patched runtime binary sitting on a node that has not been replaced may still be serving containers built before the fix.
Pull policy and RBAC are the durable controls
Patching is the immediate job. Four controls decide how much the next advisory hurts. Restrict who can create pods and import images, because several of these paths start there. Disable checkpoint and restore on nodes that do not need it. Keep CDI specifications off nodes without device requirements. Pin image digests instead of relying on tags, so a poisoned cache entry cannot pass as the intended artifact.
Revisit pull policies while you are in there. IfNotPresent is popular because it saves time and registry traffic. Cache poisoning bugs make that convenience cost more than it used to.
Container isolation is not one control. It is a stack of assumptions about trust, and a runtime that validates image references, labels, annotations and symlinks is the assumption most teams never audit.
Related reading. Why containerd and CRI-O both won the runtime war, what auditors actually ask for in a supply chain review, and how the container management market shifted toward AI workloads.
Get the next one before it is old news
Independent analysis of cloud-native infrastructure, Kubernetes and data centre economics. No vendor spin.
[…] is a stack of assumptions, and the kernel sits under every one of them. It matches the shape of the containerd CRI flaws patched earlier this month, where the newest layer kept trusting metadata it should […]
[…] reading. We looked at why Kubernetes isolation keeps breaking at the runtime layer, and at how the most used storage on Kubernetes is the one you get for free. For the observability […]
[…] reading. We looked at where isolation breaks in the container runtime layer, and at why Kubernetes for AI is a different job than Kubernetes for […]